Clarify where your cybersecurity stands.
- Strategize what needs to happen next.
- Deliver the changes your business needs.
Your situation
Gain clarity on your cybersecurity risks so you know what to prioritize.
Your organization handles data people count on, and security sits on your desk. Whether you carry it on top of everything else or it is your job, the questions are the same: are we in a sound position? Where should we start?
Often it starts with an audit, a question from the board, or an incident at a competitor. What you need then is a clear picture, a plan you can defend in front of your leadership or your board, and someone senior who stays at your side until it is delivered.
That is the work we have done since 2007, from SMBs to Crown corporations.
Organizations we have worked with
Our clients tend to stay: our longest relationships run 7.5 and 10 years, including over 50 projects with a single organization.



Services
Four ways to work with us.
Strategic Advisory
You have an audit report, a client requirement, or a critical project that needs an experienced security advisor. We turn it into a plan, and we stay until it's delivered.
See how an advisory mandate runsFractional CISO
You're responsible for security, but no one in-house leads it. We take on that role at your side: priorities, board conversations, and a security program your team can actually run.
See the fractional CISO engagementSecurity Architecture
Your project is moving fast and security decisions can't wait. We design and review the architecture with your delivery teams, with security requirements built in from the design stage.
See the architecture workCompliance
Compliance requirements are piling up: privacy regulations, client demands, insurers, ISO frameworks. We turn them into measures your team implements and can maintain, from the audit findings to daily operations.
See the compliance approach
How we work
From the first conversation to delivery.
- Clarify
Where your cybersecurity stands.
We meet your leaders, read what exists, and name the risks that actually matter to your business. You leave with a plain-language picture and a short list of what comes first.
- Strategize
What needs to happen next.
With your team, we turn that list into a roadmap your board can read: sequence, effort, owners, budget. In business terms.
- Deliver
The changes your business needs.
We stay through delivery, working with your IT and project teams at their pace, until the changes are in production.
Perspectives
Recent articles
Three Canadian Breaches in 90 Days: What Executives Should Learn from CIRO, Loblaw, and Telus Digital
In less than a quarter, Canada's investment regulator, its largest retailer, and a major telecom were all compromised. Three incidents that prove nobody is out of reach, least of all organizations that think they're too small to be targeted.
Read moreRansomware in 2026: Why 64% of Victims No Longer Pay, and What It Means for You
Ransomware is present in 44% of breaches, and in 88% of those hitting SMBs. But 64% of victims refuse to pay. Here's what changed and how to prepare.
Read moreYour Vendors Are Your Weakest Link: When Trust Becomes an Attack Vector
30% of breaches involve a third party. How to protect your organization when the threat walks in through your vendors' door.
Read more
The people behind the mandates
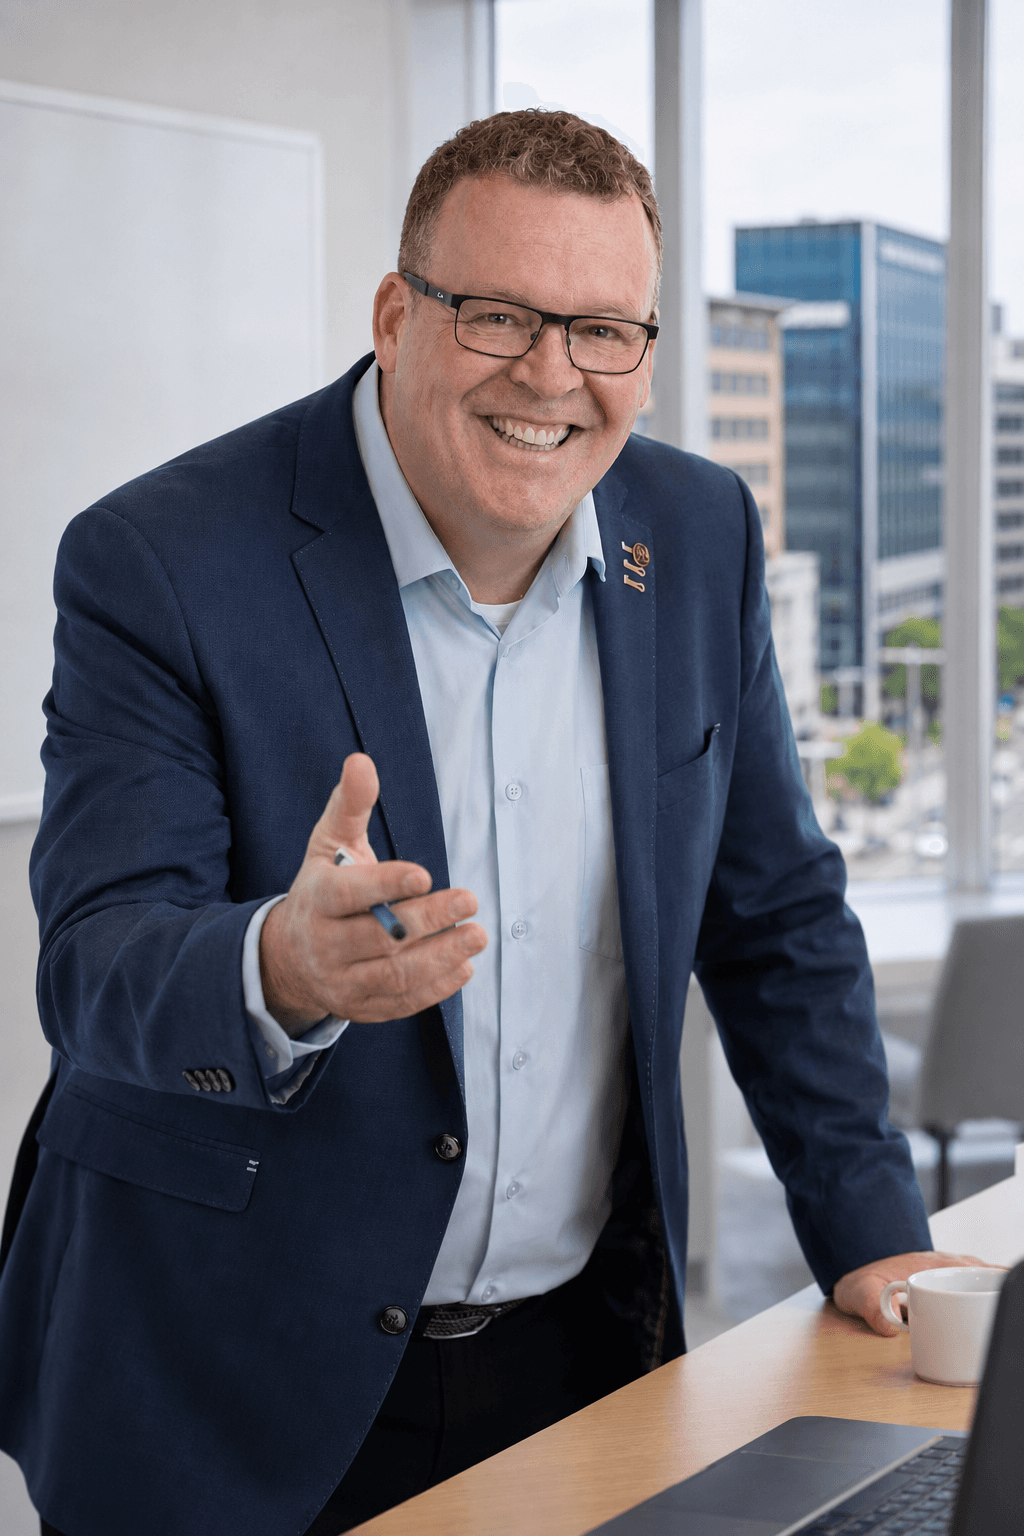
Thirty years in security, from the server room to the boardroom. Mario founded InfoSec in 2007 and stays involved in every mandate, from assessment to delivery. His experience: the hard part of any security project is getting people to decide and to work together. He wrote his first program in BASIC in grade six.
Stéphane looks after InfoSec's growth and helps clients decide where their security budget earns the most. He turns technical complexity into an investment case a board can approve, with a return it can measure. Talk to him when the question is where to put the money.


Want clarity on where you stand? Let's talk.
Tell us where you stand. We'll help you see which risks matter and where to start.
- Address
- 585, boulevard Charest Est, local 900, Québec (Québec) G1K 3J2
- Phone
- 418 476-3180 · 1 855 760-4059
Your data is used only to respond to you. Details in our Privacy Policy.
Discuss your situation
An InfoSec advisor replies within two business days. The first conversation is about understanding your situation and seeing whether we can help, with no proposal and no commitment.